Visitors to some of the world’s best-known websites were served, or potentially served, malicious code after attackers compromised a trusted tool used to test and personalise web pages.
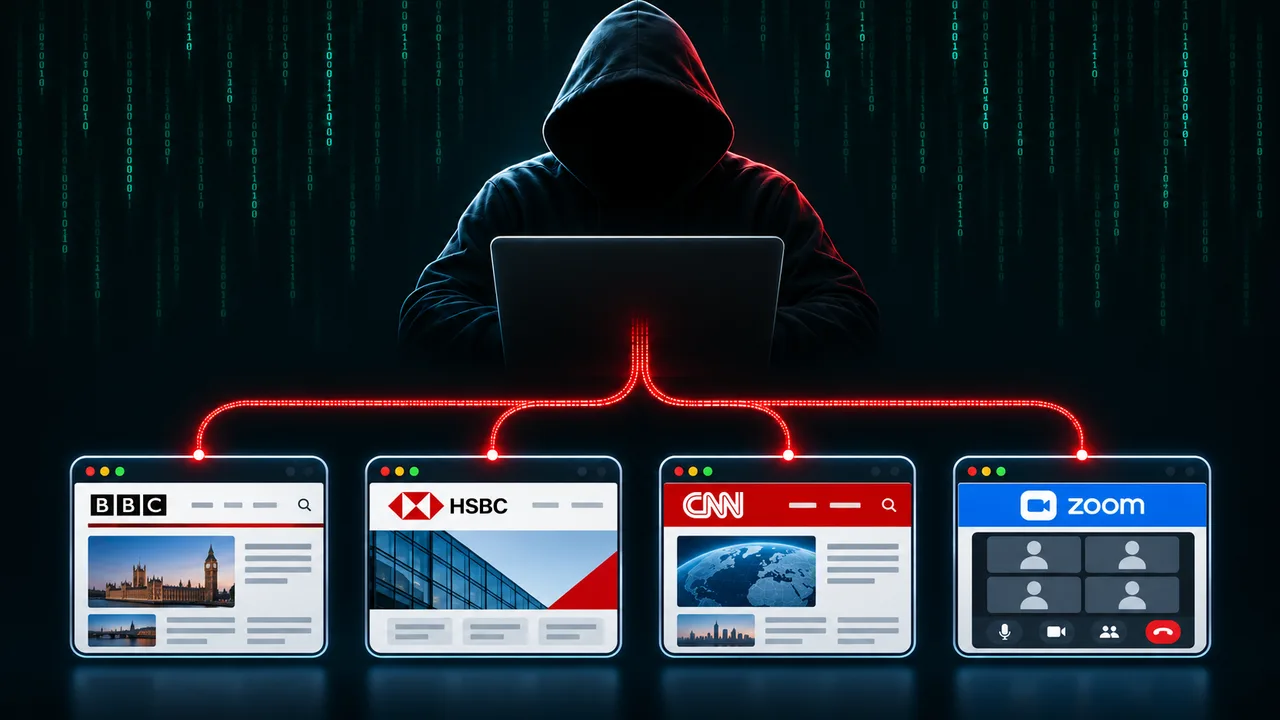
Security researcher Scott Helme and his team at Report URI examined 1,611 files from the Optimizely Web experimentation platform and found malicious code in 188 of them, linked to 178 organisations. The list included the BBC, CNN, Zoom, Salesforce, GitLab, IKEA, Equifax and HSBC-related projects.
The attack did not require hackers to break separately into every organisation. Sites load Optimizely JavaScript to run experiments and customise what visitors see. According to Report URI’s technical investigation, the attacker placed their own code inside the customer-project section of those trusted files. Browsers continued to receive the files from Optimizely’s infrastructure, allowing the malicious code to travel through a service the affected sites already trusted.
What the malicious code tried to do
The payload was designed to replace legitimate cryptocurrency wallet addresses with addresses controlled by the attacker. It could interfere with addresses displayed on a page, copied to the clipboard or sent through web requests.
Researchers also found card-skimming functions intended to capture payment details entered into some forms, along with tools for collecting cookies, page information and screenshots. On iPhones and iPads, the code attempted to deliver the Coruna and DarkSword exploit kits to older versions of iOS.
That does not mean every visitor was successfully hacked. Reuters said it could not determine whether the code succeeded in every case or establish the extent of any resulting compromise. Security researchers also cautioned that delivering an exploit to an emulated iPhone did not prove that a real device had been taken over.
How far did it spread?
Report URI traced the first observed Optimizely injection to a BBC-related file at 04:21 UTC on Monday, 16 November. The malicious payload changed repeatedly during the day as new capabilities and wallet addresses were added.
BleepingComputer independently confirmed that the script loaded, or attempted to load, through files associated with sites including the BBC, CNN, Zoom, Salesforce, GitLab and KLM. Its report also identified HSBC Insurance among affected sites. HSBC separately told Reuters that unauthorised scripts were not active on its websites.
Equifax told Reuters that it stopped using the platform and had found no evidence that its own systems were compromised. Salesforce disabled Optimizely scripts as a precaution while it investigated.
Optimizely says the flaw is fixed
Optimizely said an unauthorised party exploited a vulnerability in the signup flow for its Experimentation product and used it to add JavaScript to some customer projects.
The company said it blocked the vulnerable route, deployed a fix, removed the injected code, ended active sessions, revoked tokens and reset access for affected accounts. It also notified affected customers. Report URI said the number of infected files fell sharply during the evening and later reported that the files it had identified were clean.
Transactions worth roughly $7,000 passed through cryptocurrency wallets found in the malicious script, but some of those wallets were already active before the attack. The amount that can be attributed to this campaign therefore remains unclear.
What visitors should do
People who visited one of the affected sites on 16 November are not automatically victims. However, anyone who entered card details should monitor their statements and report unfamiliar transactions to their bank. People who made a cryptocurrency transfer should verify that the destination address was not changed.
iPhone and iPad users should install the latest available operating-system updates. Anyone who notices unexpected account activity should change the relevant password, end other active sessions where possible and enable multi-factor authentication.
The incident exposes a central weakness in the modern web: a company can secure its own servers and still deliver hostile code through a third-party service it trusts. One compromised supplier can become a route into hundreds of unrelated websites—and into the browsers of the people visiting them.